Why Partner with Mindpool for Cybersecurity

Cybersecurity consulting services
  • Mindpool Technologies empowers organizations to proactively manage cyber risk through consulting, implementation, and managed security services. As a trusted cybersecurity services provider, we help you build resilient, compliant, and future-ready security programs using industry-leading tools and proven best practices.

    Our certified security professionals combine offensive testing, managed defense, and compliance expertise to give you a complete picture of your security posture — not just an automated scan. Every engagement is mapped to recognised frameworks, scored with CVSS, and delivered with clear, prioritized remediation guidance.

    Framework-Aligned, Standards-Driven

    Our testing is mapped to OWASP, PTES, OSSTMM, NIST SP 800-115, and MITRE ATT&CK, and our delivery is backed by ISO/IEC 27001:2013 (Information Security) and ISO 9001:2015 (Quality Management) certifications — so security, quality, and confidentiality are built into every engagement.

Penetration Testing & Red Team Services

Comprehensive offensive security testing across every layer of your attack surface — tested the way real attackers operate, not just with automated scanners.

Web application penetration testing

Web Application PT

OWASP Top 10 & business-logic testing for web apps and APIs.

Mobile app penetration testing

Mobile App PT (Android & iOS)

Static/dynamic analysis, insecure storage, API & backend testing.

Thick client penetration testing

Thick Client PT

Binary, memory, local storage and client-server communication review.

Network penetration testing

Network PT

Internal & external testing, segmentation and lateral-movement checks.

Infrastructure penetration testing

Infrastructure PT

Servers, cloud infra, Active Directory and configuration hardening review.

Red teaming

Red Teaming

Goal-based adversary simulation testing people, process and technology.

Our Security Frameworks & Toolset

As your security partner, we bring deep methodology and tooling expertise across the full testing lifecycle. Our experts work across the following frameworks and platforms.

Methodologies & Standards
  • OWASPOWASP Top 10
  • PTESPTES
  • OSSTMMOSSTMM
  • NISTNIST SP 800-115
  • MITREMITRE ATT&CK
Testing Tools
  • Burp SuiteBurp Suite
  • NmapNmap
  • MetasploitMetasploit
  • OWASP ZAPOWASP ZAP
  • NessusNessus
Cloud & Infra Security
  • AWSAWS
  • AzureAzure
  • GCPGCP
  • KubernetesKubernetes
  • Active DirectoryActive Directory
Compliance & GRC
  • ISO 27001ISO 27001
  • SOC 2SOC 2
  • PCI-DSSPCI-DSS
  • GDPRGDPR

Our Security Engagement Process

From first scoping call to final sign-off, our process emphasises transparency, speed, and measurable risk reduction.

Scoping & Planning

Define assets, risk priorities, and clear rules-of-engagement for the test.

Reconnaissance & Mapping

Map your full attack surface — apps, network, cloud, and identity — as an attacker would.

Active Testing

Framework-mapped manual + tool-assisted testing to find real, exploitable vulnerabilities.

Reporting & Risk Rating

Executive summary plus technical detail, with CVSS scoring and prioritized findings.

Remediation Support

Clear, actionable fix guidance and hands-on support for your engineering team.

Retest & Sign-off

We validate fixes with a complimentary retest and confirm your improved posture.

Scoping & Planning

Define assets, risk priorities, and clear rules-of-engagement for the test.

Reconnaissance & Mapping

Map your full attack surface — apps, network, cloud, and identity — as an attacker would.

Active Testing

Framework-mapped manual + tool-assisted testing to find real, exploitable vulnerabilities.

Reporting & Risk Rating

Executive summary plus technical detail, with CVSS scoring and prioritized findings.

Remediation Support

Clear, actionable fix guidance and hands-on support for your engineering team.

Retest & Sign-off

We validate fixes with a complimentary retest and confirm your improved posture.

Scoping & Planning

Define assets, risk priorities, and clear rules-of-engagement for the test.

Reconnaissance & Mapping

Map your full attack surface — apps, network, cloud, and identity — as an attacker would.

Active Testing

Framework-mapped manual + tool-assisted testing to find real, exploitable vulnerabilities.

Reporting & Risk Rating

Executive summary plus technical detail, with CVSS scoring and prioritized findings.

Remediation Support

Clear, actionable fix guidance and hands-on support for your engineering team.

Retest & Sign-off

We validate fixes with a complimentary retest and confirm your improved posture.

Every engagement is designed to reduce real risk — measurable, prioritized, and validated with a retest.

Flexible Security Engagement Models

Get enterprise-grade security coverage on a model that fits your size, budget, and maturity.

Project-Based VAPT

Fixed-scope penetration test or audit with a clear report and retest.

SOC as a Service

24x7 managed monitoring, detection & response (MDR) and incident response.

On-Demand Pen Tester

Certified OSCP/CEH/CISSP testers embedded on contract, remote or on-site.

Security Advisory & GRC

Ongoing compliance, policy, and security-program consulting (ISO 27001, SOC 2).

Each model offers complete transparency, control, and alignment with your security priorities.
Why Partner with Mindpool

Why partner with Mindpool for cybersecurity
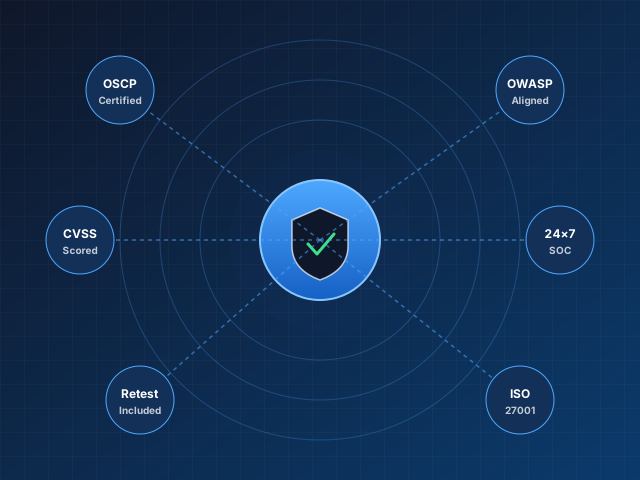
    • Certified Security Experts

      OSCP, CEH, CISSP & OSCE-certified consultants with hands-on offensive experience.

    • Framework-Aligned Methodology

      Testing mapped to OWASP, PTES, OSSTMM, NIST SP 800-115 and MITRE ATT&CK.

    • Actionable, Risk-Based Reporting

      Executive summaries plus technical depth, CVSS scoring, and clear remediation.

    • Client-Centric Engagements

      Flexible scoping, transparent communication, and a complimentary retest every time.

    • 24x7 SOC & Data Protection

      Round-the-clock monitoring and strict NDA-backed, ISO 27001-certified handling.

Frequently Asked Questions

A vulnerability assessment identifies and lists potential weaknesses; penetration testing actively exploits them to show real business impact. Mindpool delivers both — VAPT — so you know not just what is vulnerable, but what an attacker could actually do.
Talk to our VAPT team

Our testing is mapped to OWASP, PTES, OSSTMM, NIST SP 800-115, and MITRE ATT&CK, and we support ISO 27001, SOC 2, PCI-DSS, and GDPR readiness and audits.
Request a compliance-ready engagement

Every engagement includes an executive summary plus technical detail, with CVSS scoring and clear, prioritized remediation guidance — so both leadership and engineers know exactly what to do.
See a sample report

Yes. Our SOC-as-a-Service provides 24x7 monitoring, managed detection and response (MDR), and incident response, so threats are caught and contained continuously.
Explore SOC-as-a-Service

Yes. We provide certified, on-demand penetration testers on short- or long-term contracts who work within your existing workflows, remotely or on-site.
Hire a certified pen tester

Absolutely. We are ISO/IEC 27001:2013 certified, sign NDAs for every engagement, follow strict rules-of-engagement, and include a complimentary retest to validate your fixes.
Start a secure engagement
Drop Us a Line

Connect with Us

Let's connect and explore how Mindpool Technologies can secure your business and support your needs.

To More Inquiry
+91 997 266 0966
If you’re a job seeker looking to join our team, please visit our Careers page.
Otherwise, fill out the form below to Talk to our Cybersecurity Team